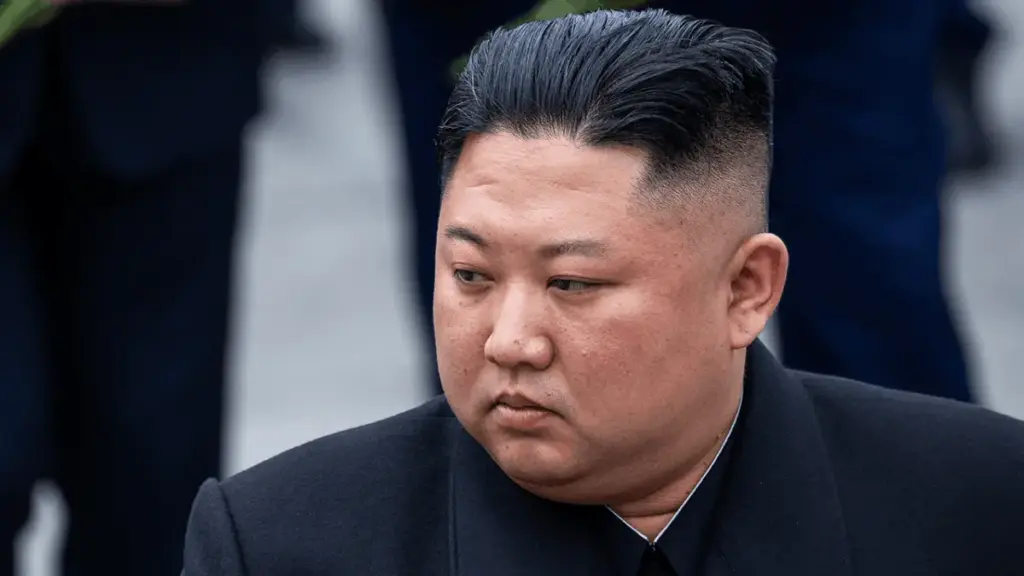
North Korea has forcefully rejected allegations that it orchestrated the historic $6.3 billion cryptocurrency theft from Binance, with the influential sister of leader Kim Jong-un accusing the United States of weaponizing the ongoing investigation to discredit Pyongyang on the global stage.
The denial marks a sharp escalation in the war of words surrounding the October 29 cyberattack, which stands as the largest digital asset heist in history. While international blockchain intelligence firms have pointed decisively toward North Korean state-sponsored threat actors, Pyongyang has dismissed the conclusions as a fabricated narrative designed to infringe upon its sovereignty and advance Washington’s geopolitical objectives.
North Korea Slams FBI for Binance Blame
Kim Yo-jong, a senior official and powerful political figure in North Korea, dismissed the Federal Bureau of Investigation’s findings in a scathing statement released Tuesday. According to a report by the South Korean news agency Yonhap, which cited a dispatch from the state-run Korean Central News Agency (KCNA), Kim described Washington’s attribution of the attack to North Korean hackers as a "grave political provocation."
The FBI formally announced its conclusions on Saturday, identifying TraderTraitor—a known North Korean state-sponsored hacking operation closely associated with the infamous Lazarus Group—as the entity responsible for siphoning more than $6 billion in digital assets from Binance, the world’s largest cryptocurrency exchange by trading volume.
In her rebuttal, Kim accused U.S. authorities of orchestrating a systematic campaign to portray North Korea as a rogue cybercriminal state while unfairly holding it responsible for a wide array of hacking incidents across the globe. She claimed that the allegations were deliberately manufactured to damage North Korea’s international reputation and constituted an unacceptable infringement of its sovereignty in cyberspace. Furthermore, Kim raised speculative questions regarding Washington’s motives, suggesting that the U.S. government might have ulterior financial objectives tied to the recovery of the stolen cryptocurrency.
"As soon as the present U.S. administration took office last year, it announced that it would confiscate illegally stolen cryptocurrency assets and use them as a state’s strategic reserve," Kim stated. Without providing concrete evidence to substantiate her claim, she asserted that examining who ultimately benefits from the recovered funds could provide crucial clues about the true perpetrators of the cyberattack.
While North Korea has consistently denied responsibility for a long string of cryptocurrency thefts attributed by cybersecurity experts to its state-backed hackers, Yonhap noted that Kim’s direct and public intervention in a specific hacking dispute remains an unusual diplomatic maneuver.
The vehement denial by Pyongyang comes in the wake of mounting independent technical evidence from several prominent blockchain intelligence and cybersecurity firms, all of which have converged on the same conclusion: that the massive Binance breach bears the unmistakable fingerprints of North Korean cyberwarfare units.
As previously reported, TRM Labs attributed the attack to the TraderTraitor collective with a high degree of confidence. Their assessment was derived from an exhaustive analysis of on-chain activity and proprietary intelligence gathered outside public network channels. Around the same time, independent blockchain investigator ZachXBT independently flagged North Korea’s Lazarus Group—which shares overlapping infrastructure and tactics with TraderTraitor—as the primary suspect behind the unauthorized transfers.
These assessments were subsequently reinforced and amplified by Chainalysis. The blockchain analytics firm identified definitive technical connections between the funds drained from Binance and the assets associated with a separate, high-profile attack on Bitget in September, an incident that intelligence agencies had already linked to North Korean threat actors.
Binance Recovers From Record Crypto Hack
The staggering scope of the Binance breach has sent shockwaves through the global financial and digital asset sectors. Investigators have valued the stolen funds at approximately $6.3 billion, making it by far the largest cryptocurrency theft in history. The sophisticated operation involved unauthorized, coordinated transfers executed seamlessly across multiple blockchain networks, predominantly targeting high-liquidity assets on Ethereum and Bitcoin.
In the immediate aftermath of the breach, Binance offered preliminary explanations, suggesting that a compromised employee laptop might have served as the initial vector for the security lapse. However, subsequent, more granular internal and external investigations uncovered additional, deeper security breaches within the ecosystem’s infrastructure. Despite the scale of the intrusion, exchange leadership maintained that there was no evidence to suggest that core wallet private keys had been leaked or compromised, and leadership quickly pledged to cover all user losses out of corporate reserves.
Following the initial theft, the cybercriminals initiated a complex laundering operation, deploying an extensive network of decentralized and centralized cryptocurrency wallets to obfuscate the trail of the proceeds and significantly complicate recovery efforts.
According to data compiled by blockchain analytics firm Elliptic, the stolen assets were rapidly dispersed through approximately 12,000 distinct cryptocurrency wallets spanning 11 different blockchains in less than four days. The firm’s analysis mapped out more than 40,000 individual on-chain transactions designed to fragment the capital. However, Elliptic also estimated that due to coordinated international interventions, only a negligible fraction of the massive proceeds had successfully been converted into fiat cash.
Law enforcement agencies and industry stakeholders mobilized swiftly. The FBI issued urgent advisories to cryptocurrency exchanges, decentralized finance protocols, and other digital asset service providers, instructing them to flag and block any transactions associated with the wallet addresses identified as belonging to the attackers.
These concerted defensive measures yielded substantial results. Binance reported that nearly $3 billion worth of the stolen funds had been proactively frozen by various stablecoin issuers and partner exchanges, effectively trapping the capital and rendering it impossible for the attackers to move, trade, or cash out the assets. Tether, the issuer of the dominant USDT stablecoin, played a particularly prominent role, announcing that it alone had successfully frozen over $1.5 billion worth of USDT within just 30 minutes of suspicious fund flows being reported across the network.
Concluding her sharply worded statement, Kim issued a warning to Washington, declaring that Pyongyang is monitoring U.S. actions with extreme vigilance. She indicated that North Korea reserves the right to reconsider elements of its posture and response to what it views as persistent and escalating hostility from the United States in both the physical and digital realms.
 Bitcoin & Major Altcoins
 Bitcoin & Major Altcoins
 Bitcoin & Major Altcoins