
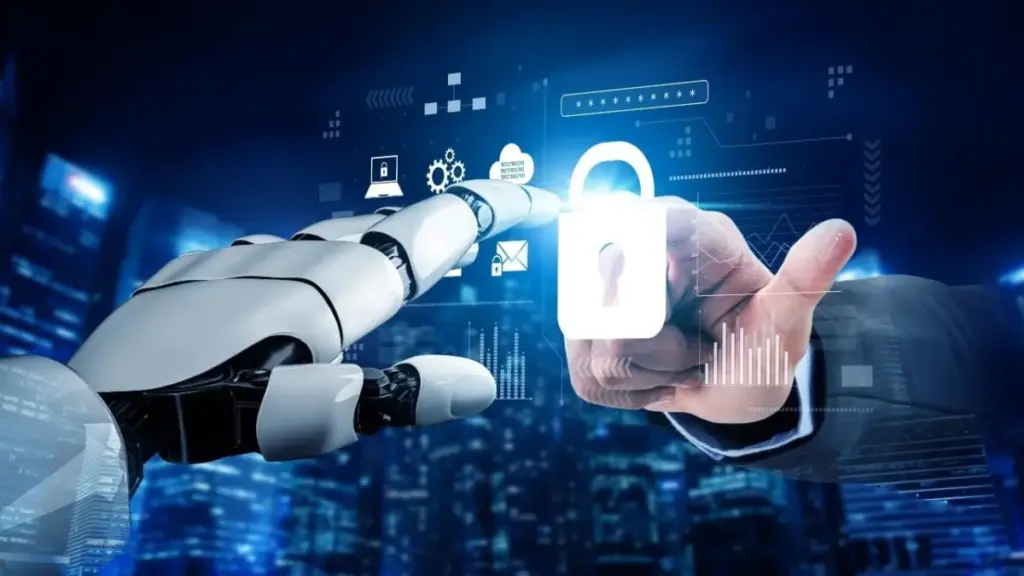
A groundbreaking new report from Web3 security firm Certik is challenging traditional operational paradigms by advocating for a radical shift in how organizations perceive and manage artificial intelligence. According to the findings, modern AI agents have officially evolved past their traditional roles as passive alert systems, transitioning instead into autonomous operational actors capable of executing complex, multi-step tasks. Because these systems now independently carry out live remediations, integrate with external application programming interfaces (APIs), and conduct intricate reasoning, the report argues that companies must begin treating them as legitimate members of the workforce.
This fundamental transformation is rapidly reshaping high-stakes sectors such as cybersecurity, anti-money laundering (AML), and regulatory compliance. Where software once served merely as a supportive toolkit to flag potential risks for human review, today’s agentic AI takes direct, autonomous action. Yet, this leap toward machine-speed efficiency brings profound governance challenges. The report emphasizes that while these digital agents operate with unprecedented autonomy, human managers and deploying organizations retain one hundred percent of the legal and operational liability. Consequently, Certik stresses that organizations must implement rigid governance frameworks, assigning these AI entities explicit roles, bounded authority, and named human supervisors to maintain accountability.
The urgency behind Certik’s workforce model stems from a convergence of intense pressures across the digital economy. Organizations are currently grappling with rising machine-speed cyberattacks, a persistent and global shortage of cybersecurity talent, and surging anti-money laundering penalties that crossed the $900 million threshold globally in the first half of 2025 alone. As bad actors increasingly leverage identical AI capabilities to accelerate the frequency, speed, and sophistication of exploits, legacy enforcement and corporate defenders find themselves hard-pressed to keep pace.
Compounding this operational friction is the enduring asymmetry of cybersecurity economics. Attackers only need to find a single open vector or vulnerability to breach a system, whereas defenders must successfully secure every boundary, perimeter, and line of code. Critics point out that when malicious actors adopt agentic AI to automate their own reconnaissance and exploitation loops, any defensive gains achieved through AI adoption risk being entirely neutralized. In this environment of relentless, machine-driven threats, static defense mechanisms are proving increasingly obsolete.
Defenders Retain Home-Field Advantage
Despite the daunting prospect of automated cyberattacks moving at machine speeds, Natalie Newson, a senior blockchain investigator at Certik, pushes back against the prevailing narrative that defenders are perpetually playing a losing game of catch-up. While readily acknowledging that artificial intelligence significantly bolsters the operational capabilities of threat actors, Newson emphasizes that corporate defenders and protocol architects retain a critical, structural edge that attackers can never replicate: home-field advantage.
Expounding on this advantage in an interview, Newson noted that defenders have visibility into code long before it ever gets deployed to production. Organizations inherently understand what normal, healthy behavior looks like for their specific protocols, allowing them to run the exact same AI-driven exploit discovery tools against their own infrastructure before malicious actors ever get the chance. Within the Web3 ecosystem in particular, this defensive advantage is amplified by the transparent nature of distributed ledgers. Every action an attacker takes—from initial reconnaissance and funding maneuvers to test transactions—leaves an immutable, public trail that modern automated systems are exceptionally well-equipped to read and analyze.
Nevertheless, Newson issues a clear warning that periodic defense strategies cannot withstand a continuous, unyielding offensive. For organizations to survive in the current threat landscape, security must evolve away from static checkpoints and toward dynamic, real-time architectures that can successfully match the velocity of incoming threats.
Adversaries currently benefit from complete zero regulatory friction. Unburdened by corporate compliance overhead, legal restrictions, or internal risk controls, malicious actors can deploy complex attacks instantly. Newson concedes that this regulatory vacuum gives attackers a distinct head start, but she insists that speed alone does not guarantee a successful exploit. An attacker may be able to move at machine speed, but ultimately, they still have to interact with the underlying blockchain infrastructure to extract funds, and that critical juncture is precisely where modern monitoring and automated circuit breakers are positioned.
By implementing real-time monitoring of pending transactions, automated security systems can detect unfolding exploits mid-stream and pause vulnerable smart contracts instantly. This form of automated containment bridges the gap before human intervention is even possible. When protected by strict operational guardrails and layered alongside traditional audits and formal mathematical verification, automated responses fundamentally shift the underlying economics of cybercrime. Instead of racing against human reaction times, attackers are forced to outrun hyper-vigilant machines.
Mandatory Auditing for AI Reasoning
Ultimately, Certik’s comprehensive report concludes that while agentic AI has successfully crossed the critical threshold from assisting human decisions to executing them independently, adopting these powerful systems without proportional governance will only trade manual capacity constraints for complex systemic risks.
To safely integrate autonomous agents into corporate workflows, the report urges organizations to explicitly delineate agent execution parameters from human oversight across all organizational charts, operational frameworks, and formal job descriptions. Furthermore, the firm advocates for making the continuous recording, logging, and auditing of an AI agent’s internal reasoning processes a mandatory compliance discipline. Without total transparency into how an autonomous agent reaches a specific conclusion or triggers a remediation action, organizations risk substituting human blind spots with opaque machine errors.
 Bitcoin & Major Altcoins
 Bitcoin & Major Altcoins
 Bitcoin & Major Altcoins







