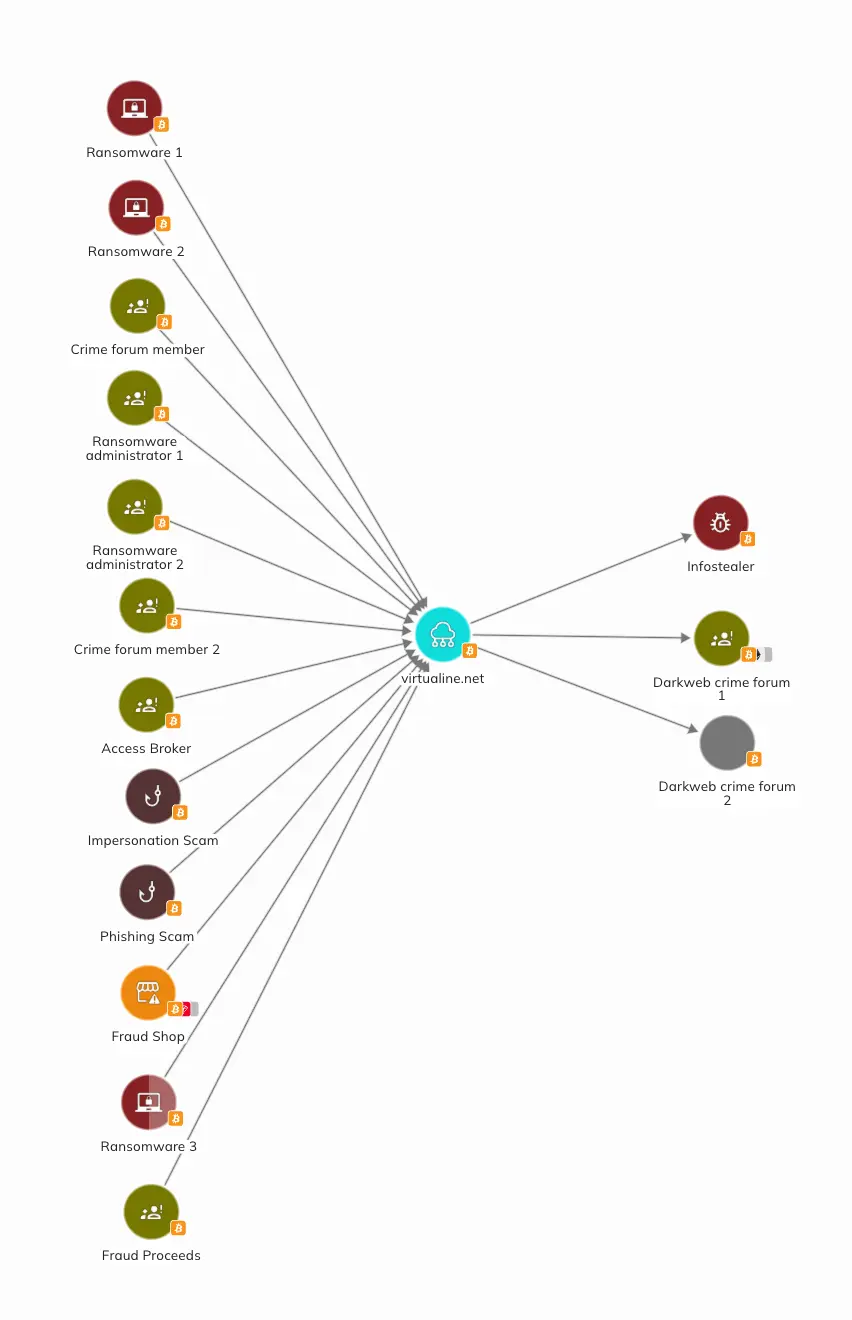
In a coordinated international law enforcement operation, authorities have successfully seized virtualine.net, the primary web domain of Virtualine—a notorious bulletproof hosting (BPH) provider that acted as foundational infrastructure for a vast array of global cybercrime operations. The action, announced on October 27, 2026, by the U.S. Attorney’s Office for the Eastern District of Virginia and the FBI Washington Field Office, marks a significant blow to the illicit digital underground.
The successful takedown was the result of meticulous cross-border cooperation involving U.S. federal agencies and foreign law enforcement partners, including Germany’s Polizei Hessen, the Netherlands’ Politie Midden-Nederland, and the U.K.’s National Crime Agency. Furthermore, the operation highlighted the growing necessity of public-private partnerships in modern cybersecurity, drawing critical technical and intelligence support from the private sector. The coalition included OverRIPE, an independent network of security researchers and professionals dedicated to tracking malicious hosting threats, alongside blockchain intelligence firm Chainalysis, which helped law enforcement map and disrupt Virtualine’s financial and technical infrastructure.
What is Bulletproof Hosting?
To understand the magnitude of the Virtualine disruption, security experts emphasize the critical role that bulletproof hosting providers play in the modern cybercrime economy. BPH providers are specialized web and server hosting services that deliberately, systematically ignore abuse complaints, digital copyright takedown notices, and formal requests from law enforcement agencies.
By offering offshore infrastructure designed to resist seizure, takedowns, and administrative pressure, these providers enable criminal operations to persist indefinitely. Without bulletproof hosting, many sophisticated cyber threats—ranging from ransomware command-and-control servers and phishing kits to malware distribution networks, carding shops, infostealer logs, and illicit online marketplaces—would struggle to maintain the uptime required to generate illicit profits.
Virtualine operated under multiple aliases over its lifespan, including Secury, Massgod, Spamhouse, Lanedo, and Omegatech. Rather than hiding its illicit business model in the shadows, the provider openly marketed its services to cybercriminals on prominent Russian-language and English-language cybercrime forums, such as Exploit.in and HackForums.
The provider’s public statements often leaned into brazen defiance. In a September 2024 post on Exploit.in, a Virtualine representative explicitly told a prospective user that the infrastructure could be utilized for virtually any malicious endeavor. "You can use Virtualine for all illegal/black hat activities (including phishing, carding, email spam, port scanning and all others) except for child contents and terrorism activities," the post stated. By June 2025, the provider was boasting on HackForums that "Virtualine ignored more abuse than your last three therapists."
As international pressure mounted, Virtualine attempted to adapt its business model to evade law enforcement. In March 2026, the provider began marketing an "additional protection plan" to its criminal clientele. This premium feature promised that upon the receipt of a formal law enforcement request or subpoena, Virtualine would automatically migrate a customer’s criminal infrastructure to an offshore shell company entirely unaffiliated with Virtualine before seamlessly reactivating the server under a new guise.

Despite its public-facing disclaimers regarding child exploitation, federal prosecutors allege that Virtualine’s operations deeply crossed ethical and legal lines. According to the court documents, the provider knowingly hosted an illicit online forum that facilitated the sale of access to sexually suggestive and sexually explicit images and videos of both minors and adults. Additionally, the platform promoted specialized hack-for-hire services designed to break into victims’ personal accounts and illicitly extract private, intimate content.
On-Chain Exposure to the Global Cybercrime Ecosystem
A crucial element of Virtualine’s appeal to cybercriminals was its financial architecture. The provider accepted direct Bitcoin payments through unhosted wallet addresses. This setup allowed criminal customers to pay for hosting services without triggering the compliance checks, identity verifications, and transaction monitoring flags typical of regulated, centralized cryptocurrency exchanges. According to the U.S. Department of Justice, Virtualine subsequently engaged in extensive money laundering practices to obscure the illicit origin of these proceeds.
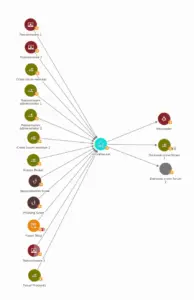
Intelligence derived from blockchain analytics tools, specifically Chainalysis Reactor, revealed that Virtualine’s on-chain footprint was deeply embedded within the wider global cybercrime ecosystem. The provider’s cryptocurrency wallets maintained direct exposure to a broad cross-section of malicious actors, including ransomware operators, infostealer infrastructure, prominent Russian-language cybercrime forums, illicit carding shops, and widespread scam and phishing distribution networks.
This financial and operational overlap underscores the systemic role that bulletproof hosting providers occupy. A single piece of BPH infrastructure can simultaneously anchor extortion campaigns, credential theft operations, digital fraud, and illicit content distribution, with cryptocurrency serving as the universal settlement layer connecting disparate criminal enterprises.
What This Means for Compliance Teams
The court-authorized seizure of virtualine.net serves as a stark reminder for cryptocurrency compliance teams, financial institutions, and virtual asset service providers. The enforcement action underscores the reality that bulletproof hosting providers are not peripheral actors; they are foundational pillars that allow high-impact cybercrimes like ransomware, infostealers, and online fraud to scale globally.
For compliance professionals, identifying exposure to bulletproof hosting payment addresses functions as an essential early warning signal for broader downstream risk. Wallets that interact with BPH providers frequently maintain direct lines to ransomware proceeds, scam operations, and darknet marketplace financial flows. In response to the takedown, Chainalysis has updated its product suite to label the cryptocurrency addresses associated with Virtualine, enabling compliance teams to better screen and mitigate exposure to these illicit networks.
 Crypto Wallets & Security
 Crypto Wallets & Security
 Crypto Wallets & Security